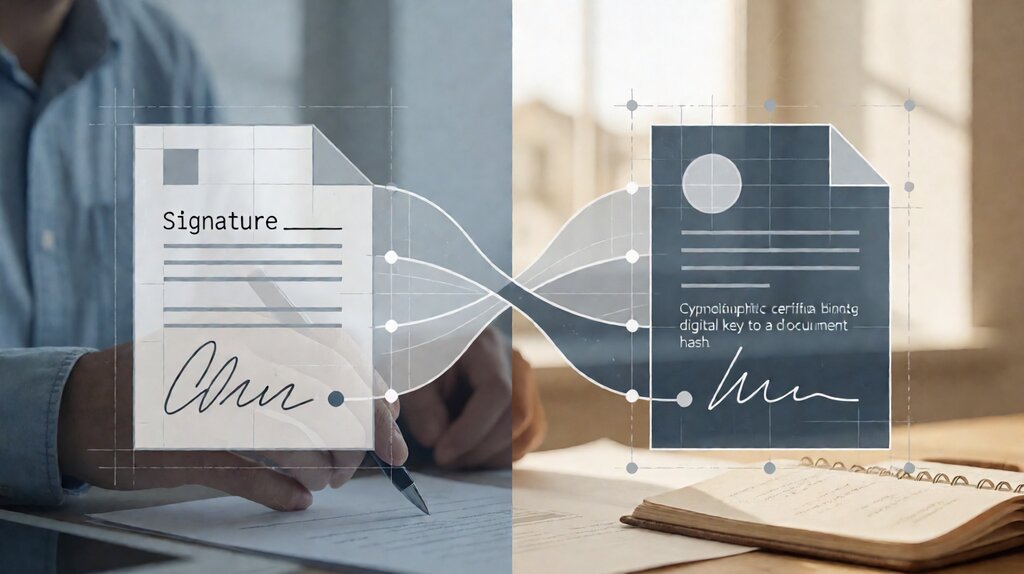

Electronic signature (e-signature) is the broad legal category of capturing a person’s intent to sign a document using an electronic process.
Digital signature is a specific subset of electronic signature that uses cryptographic certificates (Public Key Infrastructure, or PKI) to bind the signer’s identity to the document, detect tampering after signing, and provide non-repudiation stronger than the simple electronic capture.
All digital signatures are electronic signatures; not all electronic signatures are digital signatures.
Run a quick stress-test: every contract you sign through DocuSign, HelloSign, or Adobe Sign is an electronic signature at the simple tier.
The signature image is captured, an audit trail is recorded, and the document is locked.
A digital signature happens when the platform uses a cryptographic certificate issued by a trusted Certificate Authority (CA) to apply a mathematical transformation to the document hash; the resulting signature is verifiable as long as the CA is in the trust chain.
Adobe Acrobat’s PDF signature, Microsoft Authenticode, and DocuSign’s enterprise-tier signing all use digital signatures; the entry-tier DocuSign and HelloSign are electronic signatures without cryptographic certificates on every envelope.
An electronic signature is any electronic capture of intent to sign. A digital signature is a cryptographic signature bound to a PKI certificate issued by a trusted authority. Use electronic signature for most contracts; use digital signature when the contract requires it (regulated industries, federal filings, EU qualified tier).
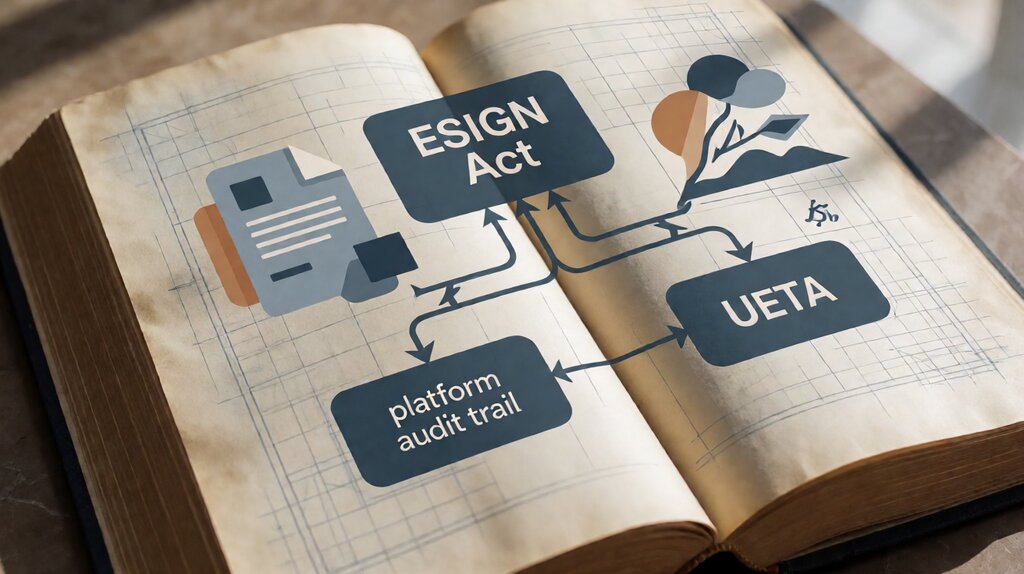
Key facts: Electronic signature is the legal category under ESIGN Act (US, 2000) and UETA (US state-level, 1999).
Digital signature is a cryptographic implementation using PKI certificates from trusted Certificate Authorities (DigiCert, Sectigo, IdenTrust, etc.).
ESIGN and UETA do NOT require digital signatures specifically; they only require the captured intent + consent + record.
The eIDAS framework (EU, 2014) requires digital signatures for the advanced and qualified tiers; the simple tier under eIDAS allows electronic signatures broadly.
For most US SMB contracts (NDAs, sales contracts, HR offer letters, contractor agreements), an electronic signature through DocuSign, HelloSign, or Adobe Sign is the entire requirement. ESIGN gives the platform’s audit trail the same evidentiary weight as a wet-ink signature. A digital signature through PDF infrastructure is needed only for contracts that require the higher PKI-based evidentiary weight (federal filings, some healthcare, some financial services).
The structural distinction in plain language
Both terms are widely used in marketing copy and often conflated. The structural distinction is about whether cryptographic certificates are involved.
| Dimension | Electronic signature (broad) | Digital signature (PKI subset) |
|---|---|---|
| Legal standing in the US | Yes, under ESIGN Act and UETA | Yes (more rigorous evidence) |
| Legal standing in the EU | Simple tier only under eIDAS | Advanced + qualified tier under eIDAS (mandatory for some regulated industries) |
| PKI certificate required | No | Yes (from trusted CA) |
| Tamper detection | Platform audit trail handles it | Cryptographic hash detects any post-signing modification |
| What a small business uses | DocuSign, HelloSign, Adobe Sign, SignNow, PandaDoc (default tier) | Adobe Acrobat Pro Sign, DocuSign enterprise, eIDAS qualified providers |
| Cost implication | $10-$50/month subscription or per-envelope fees | Per-signature certificate cost ($1-$20 each) + platform subscription |
| When to use | NDAs, sales contracts, HR paperwork, contractor agreements | Federal filings (FDA, FCC, SEC), HIPAA-BAA, EU qualified-tier, real estate in some EU jurisdictions |
For the structural distinction at depth including the cryptographic specifics of X.509 certificates and the compliance regime differences between ESIGN, UETA, and eIDAS, the electronic signature laws ESIGN Act page covers the regulatory framework in detail.
What digital signatures add on top of electronic signatures
Digital signatures are electronic signatures with three additional capabilities layered on top. The capabilities matter when the contract needs stronger non-repudiation than what ESIGN’s audit trail alone provides.
Cryptographic binding to the signer’s identity. A digital signature uses the signer’s private key (held in a hardware token or digital certificate) to sign the document hash; the corresponding public key (in the signer’s certificate) verifies the signature.
The certificate is issued by a trusted Certificate Authority that has already verified the signer’s identity.
This is the PKI infrastructure most people have encountered with TLS/SSL on websites.
Tamper detection beyond audit trail. An electronic signature’s audit trail records the document hash at signing time; if the document is modified after signing, the audit trail can be cross-referenced against a re-computed hash to detect modification. A digital signature’s cryptographic binding makes this detection automatic: any post-signing modification breaks the signature. The higher evidentiary weight comes from this property.
Non-repudiation stronger than audit trail. Under ESIGN, a signer who can show they never consented to electronic signing or whose identity was misused can potentially challenge the signature in court (the audit trail is evidence but is not cryptographically undeniable).
Under a digital signature with PKI, the signer’s certificate + private key + signed document hash is technically non-repudiable, though courts still consider operational context (was the private key in the signer’s control at the time).
When each one applies in practice
Three operating scenarios make the distinction matter.
NDAs, sales contracts, contractor agreements. Electronic signature, simple tier. The platform’s audit trail makes the contract enforceable. DocuSign, HelloSign, Adobe Sign, SignNow, PandaDoc, BoldSign all offer this tier.
Healthcare paperwork above HIPAA technical-safeguard level. Electronic or digital signature, depending on the document type and HHS guidance. For HIPAA Business Associate Agreements (BAAs), either tier is accepted by HHS; for healthcare provider-patient consent forms, electronic signature is acceptable when the platform records the audit trail sufficiently.
Federal filings (FDA, FCC, SEC, EPA) and financial regulatory paperwork. Often requires digital signature with a PKI certificate issued by a US Federal PKI bridge or a comparable authority. Adobe Acrobat Pro with a digital ID; DocuSign FedRAMP-authorized; Adobe Sign FedRAMP-authorized; specific government platforms for specific filings.
EU qualified-tier contracts (real estate in some EU jurisdictions, certain healthcare documents). Digital signature required via a qualified trust service provider (eIDAS Article 3 tier 3) using a certified hardware token. National implementations vary; for example, Spain’s FNMT and Italy’s AgID operate qualified trust lists.
How the marketing copy conflates them
The terms get used interchangeably because the legal effect is often the same (both are signatures on a contract) and the technical implementation is invisible to most users. Three places where the conflation hurts a small business.
Confusion 1: “Digital signature” in product marketing. When a vendor’s product page says “digital signature”, they typically mean electronic signature with platform audit trail, not PKI cryptographic binding. Read the vendor’s compliance documentation (DocuSign’s is at trust.docusign.com, Adobe Sign’s is at adobesign.adobe.com/security) to confirm the actual cryptographic tier.
Confusion 2: Certifying authority and Certifying Provider. “Certificate Authority” (CA) is a PKI trust provider (DigiCert, Sectigo). “Trust Service Provider” is an EU eIDAS provider. Both issue certificates but operate under different legal regimes; US PKI and EU eIDAS do not interoperate without explicit cross-recognition.
Confusion 3: DocuSign certificate tier. DocuSign’s enterprise tier adds PKI cryptographic signatures (eIDAS-advanced compliant) under the eIDAS Advanced tier; the standard tier is e-signature with audit trail only. Same product name, different cryptographic tier. Verify on the contract page.
Practical implications for a US SMB
The decision rule for most US SMBs is straightforward: use the electronic signature tier for 95% of contracts. Reserve digital signature for the small subset of contracts that have regulatory requirement for it (HIPAA-BAA, federal filings, certain financial services paperwork).
The cost difference is meaningful. Electronic signature through DocuSign Personal (free for one sender, 5 envelopes) or HelloSign Free (3 envelopes per month) is materially cheaper than Adobe Acrobat Pro Sign (~$25/month per user for the digital signature tier) plus a digital certificate purchase (~$20-$200/year). For a small business that signs fewer than 50 envelopes a month, electronic signature is the dominant cost answer.
For the cost math at your envelope volume and the per-tier trade-off, the electronic signature cost page covers the math. For the practical 3-way comparison of DocuSign, HelloSign, and Adobe Sign on tier-price-features, the DocuSign vs HelloSign vs Adobe Sign page runs the comparison.
For the broader vendor comparison and what each provider actually delivers at the entry tier versus the enterprise tier, the best e-signature tool for small business comparison covers the practical differences at each plan.
Last updated: October 2026